Research Security: In a Crowded Marketplace of Tools, Here’s What to Prioritize
The constellation of tools available to research security professionals is massive – and for good reason. Securing America’s innovation enterprise from malicious actors and foreign adversaries is a huge problem space with multiple vendors approaching it from different angles. Some take a purely due diligence-based approach, some adapt existing bibliometric network analysis (BNA) tools for research security purposes, and some build their own tools in-house.
For some vendors, the lowest barrier to entry involves matching their technology with your issue, when it should work exactly the opposite way. Protecting research from national security and economic risk requires understanding in real-time who is working on critical research activities, what direct and indirect connections they have and how many degrees those connections are removed from those with nefarious intentions.
In our work at Finch AI, and as part of the SECURE Analytics partnership with the National Science Foundation, we believe that any research security solution should align with specific customer needs and research security priorities in order to secure the innovation enterprise. Here’s how to assess if a solution or tool set you’re considering does exactly that:
Start with mission requirements, not vendor features. A credible research security solution must map to your research security program objectives (risk identification, adjudication support, mitigation recommendations, continuous monitoring, reporting, etc.) and withstand audit and executive scrutiny not simply “match” a point tool to a headline problem.
Demand full-context visibility across people, organizations, and networks. Effective due diligence requires entity resolution plus relationship mapping (direct and indirect ties), surfacing the “degrees of separation” that often define real-world risk exposure in research collaborations.
Insist on formal critical research taxonomy mapping – because most platforms don’t have it. Today there is no widely adopted, authoritative mapping that translates U.S. Critical and Emerging Technologies (CET) into standardized research subject taxonomies (e.g., ASJC) in a way that can be operationalized for real-time monitoring; nor is there a structured comparison to China’s State Council Academic Degree Committee (SCADC) taxonomy. Without this crosswalk, institutions and vendors lack a defensible, repeatable method to identify, understand, and continuously monitor who is working in critical technology areas leaving a foundational gap in many BNA and research security platforms.
Require operational workflow support, not just data. The right solution accelerates decision-making with configurable risk questions, comprehensive risk assessments, evidence traceability, and outputs that are easy to brief to research leadership, compliance, and/or legal teams.
Evaluate vendors on adaptability and trust. Threats, policy expectations, and data sources evolve so prioritize platforms with a trusted disambiguation and entity-resolution process and policy-native configurability (institutional, sponsor, and regulatory). Look for continuous updates, explainable outputs, and repeatable workflows so determinations stay consistent, auditable, and defensible over time.
Each year, adversaries inflict hundreds of billions of dollars of economic damage to American institutions and corporations by unlawfully accessing academic and corporate research to steal innovation or disrupt the operation of our critical infrastructure.
If your role involves protecting against these threats and securing informational assets, the priorities outlined above will be critical guideposts as you search for technology partners. To learn more about how Finch AI can help, please get in touch at info@finchai.com and if you are attending the 2026 Academic Security and Counter Exploitation (ASCE) Seminar, I will be presenting on this topic in a TechTalk on Wednesday, February 25 from 245-330pm CT in the Laurel Meeting Room.
###
Share
Eric Schweser, Director, Counterintelligence & Research Security Solutions
Discover More
Superpower Your Elasticsearch: Entity Resolution, Done In a Single Sprint
Your Analysts Are Searching, But Are They Finding Everything? A missed entity isn't just a trivial search error – it is a missed threat.…
FOIA Request Management: Done Quickly, Comprehensively and Easily With Finch for Text
High Stakes, Low Tolerance for Error When a FOIA request lands, the clock starts immediately. Your team has just 20 days to generate a…
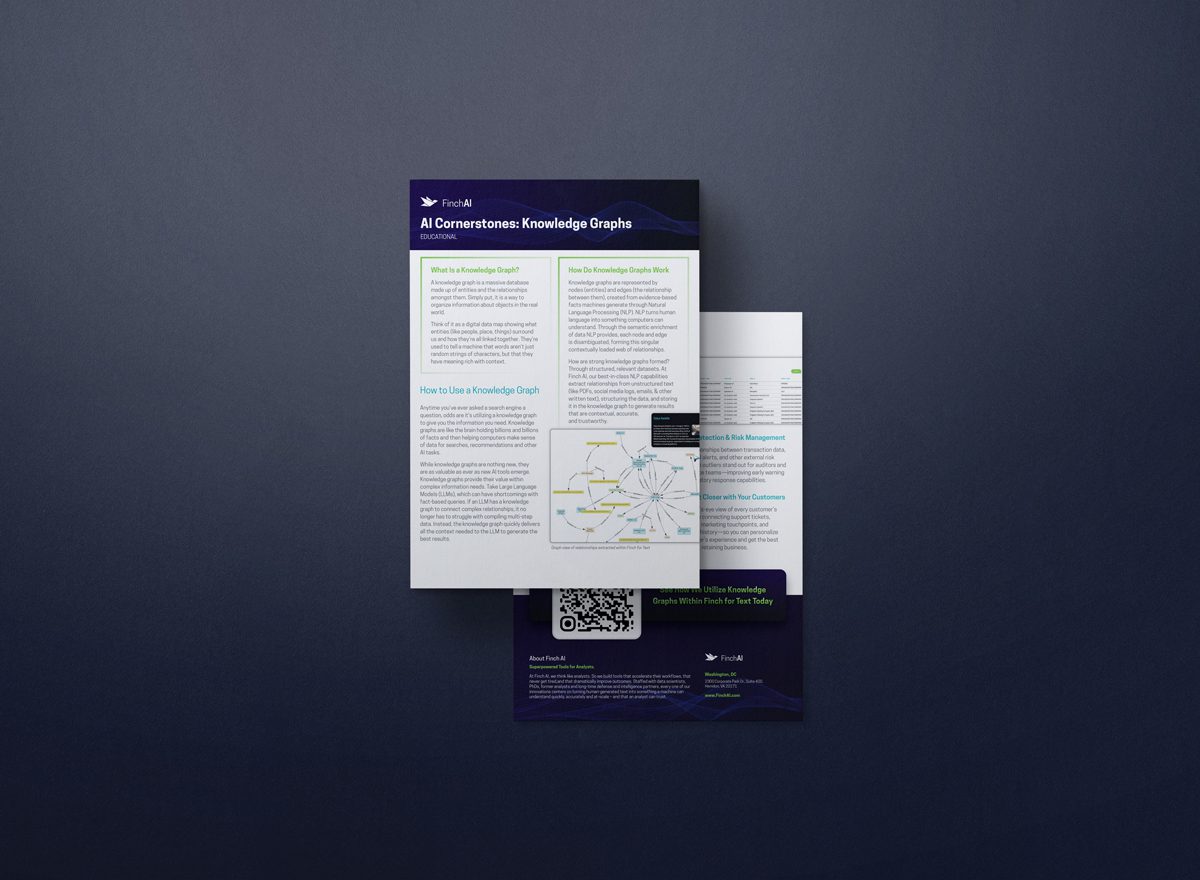
AI Cornerstones: Knowledge Graphs
Your Digital Data Map for Finding Relationships Generative AI and large language models are continuously advancing in mention and capability, but the underlying technology…
Operationalizing AI: Knowledge Graphs and AI Engineering
Following a November session on AI Agents, Finch AI and Carahsoft are pleased to present the second webinar in an educational series on operationalizing…
Research Security: Aligning Policy, Practice and Priorities to Secure the Innovation Enterprise
The U.S. faces growing challenges in protecting its innovation, research and development (R&D) enterprise, supply chain, critical infrastructure and investment capital from foreign influence,…
Research Security Realities and How to Overcome Them
Every year, our adversaries inflict hundreds of billions of dollars of economic damage to U.S. institutions and corporations. They do it by unlawfully accessing…
Research Security: In a Crowded Marketplace of Tools, Here’s What to Prioritize
The constellation of tools available to research security professionals is massive – and for good reason. Securing America’s innovation enterprise from malicious actors and…
National Science Foundation’s SECURE Analytics Initiative Expands to Include Innovative AI Partner Finch AI
Finch AI's Artificial Intelligence Capabilities to Enable and Accelerate Enhancements to Critical Research Security Platform College Station, TX - After a successful first year…