Research Security: Aligning Policy, Practice and Priorities to Secure the Innovation Enterprise
The U.S. faces growing challenges in protecting its innovation, research and development (R&D) enterprise, supply chain, critical infrastructure and investment capital from foreign influence, intellectual property theft and national security vulnerabilities. The problem is widespread and poses both an economic and national security threat.
Yet, among the major funding agencies such as the Department of War, the Department of Homeland Security, the National Science Foundation, the National Institutes of Health, the Department of Energy, as well as American businesses small and large, there is no standardized decision matrix for identifying, evaluating or addressing research security risks. The absence of shared operational tools and cross-agency coordination weakens the collective ability to secure the U.S. innovation enterprise against persistent and evolving threats.
However, there is a way to help meet this growing and evolving threat to American security and prosperity while also helping organizations meet the forthcoming regulatory requirements presently under review. As part of the SECURE Analytics partnership with the National Science Foundation, we are working to do precisely that. Here’s how:
Recognize the operational challenge. As mentioned above, there is no unified, standardized risk decision matrix for research security. Across federal sponsors, research institutions, and industry partners, expectations are rising but risk identification and adjudication remain inconsistent because programs lack a shared, repeatable decision framework. Creating one will require policymakers, subject matter experts and mission partners familiar with the unique requirements of operating in sensitive, government environments.
Supporting the current regulatory momentum. Policy solutions at-play are generally converging on “defensible, auditable, and consistent” practice. As agencies refine requirements, institutions will increasingly need documented decision logic, evidence traceability, and standardized workflows that can withstand oversight while supporting legitimate collaboration. There is a role for technology providers and the research security industry to play here as well, and engaging will create solutions that are workable, effective and sustainable as well.
Advancing a matrixed, partnership approach across the ecosystem. This will standardize practices and accelerate progress. Today, at Finch AI, we are coordinating with stakeholders including the National Science Foundation, the Department of Energy, the Hoover Institution at Stanford University, the Research and Innovation Security and Competitive Institute at Texas A&M University, and other research security offices to develop a decision matrix from the ground up— one that is rooted in operational realities and designed for cross-institution applicability.
Integrating institutional frameworks with federally released risk matrices to formalize consistency. By aligning organizational program needs with federal risk frameworks, we at Finch AI are enabling a more structured method to help partners and customers identify, evaluate and monitor risk. This supports both the current mission and future readiness for any forthcoming compliance expectations. Doing this ensures that there can be swift and seamless operationalizing of the policy solutions designed to protect the innovation enterprise.
Without question, we can secure the research enterprise – and there’s never been a better time to do it. The need is real, the urgency is growing, and the advent of AI-driven technology means we can do more and have even more of an impact. We can deliver the right intelligence at the right time – in real-time and at scale and with actionable insights that research security professionals can use and can trust.
To learn more about how Finch AI is solving this exact challenge, please get in touch at info@finchai.com.
###
Share
Eric Schweser, Director, Counterintelligence & Research Security Solutions
Discover More
Superpower Your Elasticsearch: Entity Resolution, Done In a Single Sprint
Your Analysts Are Searching, But Are They Finding Everything? A missed entity isn't just a trivial search error – it is a missed threat.…
FOIA Request Management: Done Quickly, Comprehensively and Easily With Finch for Text
High Stakes, Low Tolerance for Error When a FOIA request lands, the clock starts immediately. Your team has just 20 days to generate a…
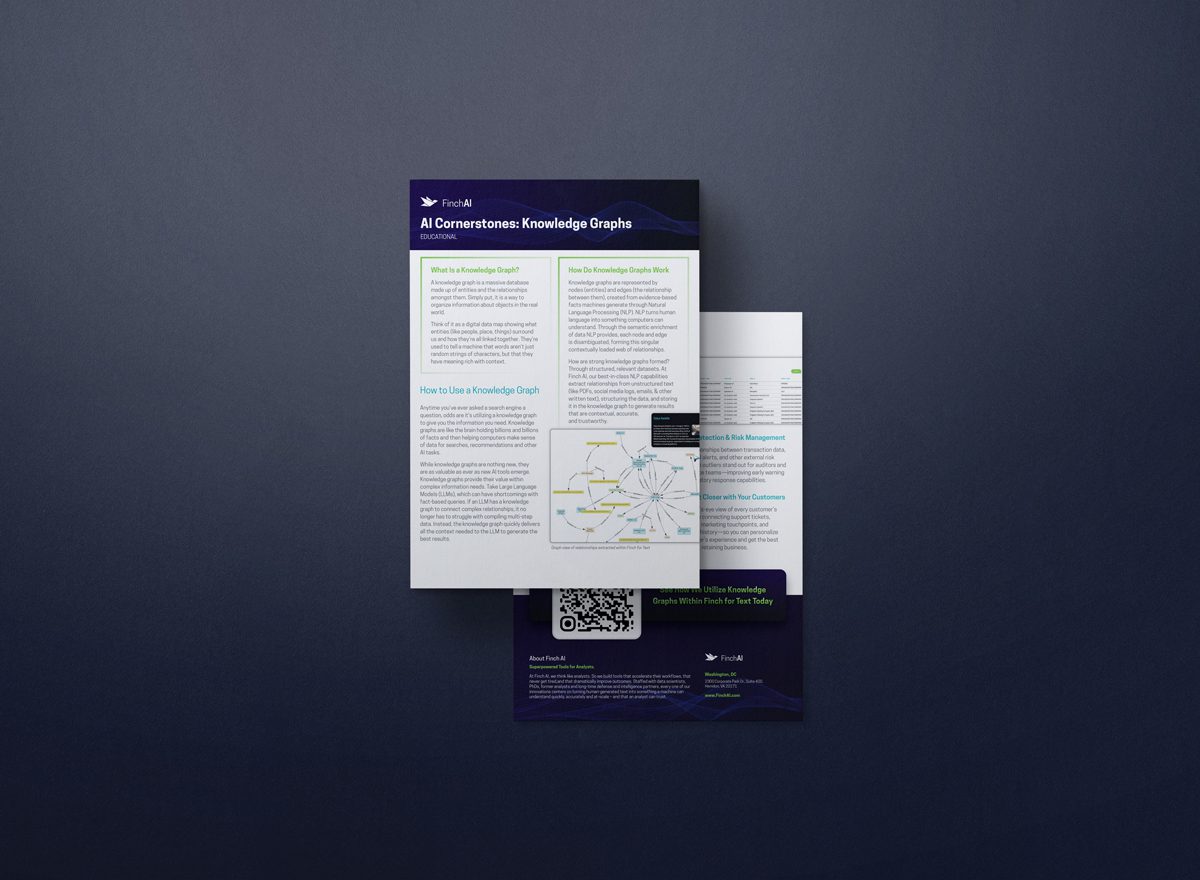
AI Cornerstones: Knowledge Graphs
Your Digital Data Map for Finding Relationships Generative AI and large language models are continuously advancing in mention and capability, but the underlying technology…
Operationalizing AI: Knowledge Graphs and AI Engineering
Following a November session on AI Agents, Finch AI and Carahsoft are pleased to present the second webinar in an educational series on operationalizing…
Research Security: Aligning Policy, Practice and Priorities to Secure the Innovation Enterprise
The U.S. faces growing challenges in protecting its innovation, research and development (R&D) enterprise, supply chain, critical infrastructure and investment capital from foreign influence,…
Research Security Realities and How to Overcome Them
Every year, our adversaries inflict hundreds of billions of dollars of economic damage to U.S. institutions and corporations. They do it by unlawfully accessing…
Research Security: In a Crowded Marketplace of Tools, Here’s What to Prioritize
The constellation of tools available to research security professionals is massive – and for good reason. Securing America’s innovation enterprise from malicious actors and…
National Science Foundation’s SECURE Analytics Initiative Expands to Include Innovative AI Partner Finch AI
Finch AI's Artificial Intelligence Capabilities to Enable and Accelerate Enhancements to Critical Research Security Platform College Station, TX - After a successful first year…